
The Urethane Blog
June 21, 2021
Indorama is in talks to buy Oxiteno
A purchase of the Brazilian specialty chemical firm would plunge the polyester producer deeper into surfactants
by Alexander H. Tullo
June 18, 2021
 Credit: Oxiteno Oxiteno’s new surfactants plant in Pasadena, Texas
The Thai chemical maker Indorama Ventures has entered exclusive negotiations with the Brazilian conglomerate Ultrapar Participações to buy Ultrapar’s specialty chemical business, Oxiteno.
The parties have yet to hammer out a purchase agreement. “Conditions of the transaction, including value, are still under consideration,” Ultra says.
Oxiteno is one of the linchpins of Brazil’s chemical industry. Among its key products are surfactants, solvents, glycols, ethanolamines, fatty alcohols, glycerin, and fatty acids. It earned $70 million in 2020 on $1.0 billion in sales. Its assets are valued at $1.7 billion.
In recent years, the company has been branching out of its home country. Its biggest such move came in 2018, when it started up a $150 million ethoxylation unit in Pasadena, Texas, on the site of a former vitamin E plant. Oxiteno claims to be the world’s second largest producer of ethoxylated chemicals, behind BASF.
Indorama has grown over the past 2 decades into a global giant in polyethylene terephthalate (PET) resins and fibers. Its sales last year were about $10 billion. And as it built its polyester business, the company became involved in surfactants as well, a direction it has embraced as a diversification maneuver.
In 2012, Indorama bought Old World Industries, a producer of ethylene glycol—a PET raw material—in Clear Lake, Texas. That plant also makes ethylene oxide, the raw material needed for ethoxylated surfactants. Indorama subsequently strengthened the business by buying and refurbishing an ethylene plant to back-integrate ethylene oxide production.
In January 2020, Indorama built on this foundation when it completed the purchase of Huntsman’s chemical intermediates and surfactants unit, a competitor to Oxiteno. That $2.1 billion deal gave Indorama plants in Chocolate Bayou, Dayton, and Port Neches, Texas, and in India and Australia.
https://cen.acs.org/business/mergers-&-acquisitions/Indorama-talks-buy-Oxiteno/99/web/2021/06
June 21, 2021
NEW IROGRAN® TPU GRADE FROM HUNTSMAN HAS IMPROVED PROPERTIES FOR FIRE HOSES AND TEXTILES
THE WOODLANDS, TX– Specialty Elastomers experts from Huntsman have developed a new thermoplastic polyurethane (TPU) grade for technical extrusion parts and blown film applications that offers significant improvements over previous generation technologies when it comes to durability, production efficiency and reducing manufacturing waste. IROGRAN® A 85 P 4394 HR TPU is the latest addition to a well-established family of elastomer products from Huntsman, which are renowned for their performance in a diverse range of industrial and consumer applications.
Developed in close partnership with Huntsman’s customers, IROGRAN® A 85 P 4394 HR TPU has greater tensile strength than the standard IROGRAN® A 85 P 4394 elastomer grade originally developed in 2004. The new grade also offers improved film extrusion quality and high melt strength, which makes it ideal for blown film applications. Delivering better resistance to force in its melted state, which makes it less likely that an extruded film will break during production, IROGRAN® A 85 P 4394 HR TPU can help to significantly lower scrap rates, improve manufacturing throughput and cut waste in blown film processing.
IROGRAN® A 85 P 4394 HR TPU is developed to solve the problems of customers in diverse markets including:
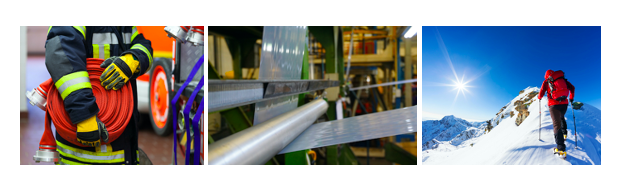
- TPU lay flat hoses used in high pressure industrial and municipal applications e.g., firefighting
- Textile lamination – as a breathable, waterproof layer for rugged performance apparel.
In the manufacture of TPU lay flat hoses, IROGRAN® A 85 P 4394 HR TPU is applied via the “extrusion through-the-weave” process. In this application, the product’s greater tensile strength is highly advantageous – helping the resulting hoses cycle between periods of being tightly coiled and then extended and put under high water pressure levels. In the case of fire hoses, this pressure can typically be in the region of 8 and 20 bar (800 and 2000 kPa; 116 and 290 psi).
When it comes to textile lamination, IROGRAN® A 85 P 4394 HR TPU is an excellent material for creating a waterproof, breathable film in rugged performance apparel (including gloves and footwear). Blown to create an extremely thin layer, which is then added to fabrics, IROGRAN® A 85 P 4394 HR TPU provides the protective properties needed to create high performance outdoor garments. Adhering well to different kinds of fabrics, IROGRAN® A 85 P 4394 HR TPU can aid the stretch and recovery of the materials it is used on. The nature of the grade also means the resulting films can be engineered to have different surface finishes, including gloss, smooth and matte effects
Trent Shidaker, Global Marketing Director, Elastomers at Huntsman, said: “IROGRAN® A 85 P 4394 HR TPU is a highly versatile and durable elastomer. Soft to the touch, it’s ideal for apparel applications that need to stay in contact with the wearer for hours at a time; but it’s also strong enough to be used in municipal and industrial hoses that have to perform under the toughest conditions. Applying its development expertise, our elastomers team has enhanced the processing properties of IROGRAN® A 85 P 4394 HR TPU, without compromising the key performance attributes expected of products in this range – namely excellent hydrolytic resistance; fantastic wear performance; and microbial resistance. The result is an elastomer that can enable manufacturers to work more efficiently, cut waste and create longer-lasting products; a compelling proposition for the markets we serve.”
The basis of the chemistry of IROGRAN® A 85 P 4394 HR TPU goes back to 2004 when the flagship product was first developed. Later variations of the product were developed to create the family of elastomer products from Huntsman that customers have learned to know and love.
Other IROGRAN® A 85 P 4394 TPU products available from Huntsman include:
- IROGRAN® A 85 P 4394 – a legacy product, launched in 2004, that was first introduced for thin wall technical parts, thin wall extrusion profiles, spiral hoses, cable jacketing and film and sheet
- IROGRAN® A 85 P 4394 FCM – launched in 2015, this grade has a similar base chemistry to the standard version of IROGRAN® A 85 P 4394 but is formulated with raw materials that are compliant with FDA regulations for food processing belts and has an NSF 61 rating (approved for potable water applications).
- IROGRAN® A 85 P 4394 UV – also launched in 2015, this product is fortified with proprietary additives that enable it to withstand UV exposure while maintaining excellent physical properties and appearance. This product is used for pneumatic tubing for airlines and industrial equipment and fracking hoses.
IROGRAN® A 85 P 4394 HR TPU is made at the Huntsman Polyurethanes manufacturing facility in Ringwood Illinois. For more information about the full range of IROGRAN A 85 P 4394 TPU products available from Huntsman, please contact: joanna_marzec@huntsman.com.
June 21, 2021
NEW IROGRAN® TPU GRADE FROM HUNTSMAN HAS IMPROVED PROPERTIES FOR FIRE HOSES AND TEXTILES
THE WOODLANDS, TX– Specialty Elastomers experts from Huntsman have developed a new thermoplastic polyurethane (TPU) grade for technical extrusion parts and blown film applications that offers significant improvements over previous generation technologies when it comes to durability, production efficiency and reducing manufacturing waste. IROGRAN® A 85 P 4394 HR TPU is the latest addition to a well-established family of elastomer products from Huntsman, which are renowned for their performance in a diverse range of industrial and consumer applications.
Developed in close partnership with Huntsman’s customers, IROGRAN® A 85 P 4394 HR TPU has greater tensile strength than the standard IROGRAN® A 85 P 4394 elastomer grade originally developed in 2004. The new grade also offers improved film extrusion quality and high melt strength, which makes it ideal for blown film applications. Delivering better resistance to force in its melted state, which makes it less likely that an extruded film will break during production, IROGRAN® A 85 P 4394 HR TPU can help to significantly lower scrap rates, improve manufacturing throughput and cut waste in blown film processing.
IROGRAN® A 85 P 4394 HR TPU is developed to solve the problems of customers in diverse markets including:
- TPU lay flat hoses used in high pressure industrial and municipal applications e.g., firefighting
- Textile lamination – as a breathable, waterproof layer for rugged performance apparel.
In the manufacture of TPU lay flat hoses, IROGRAN® A 85 P 4394 HR TPU is applied via the “extrusion through-the-weave” process. In this application, the product’s greater tensile strength is highly advantageous – helping the resulting hoses cycle between periods of being tightly coiled and then extended and put under high water pressure levels. In the case of fire hoses, this pressure can typically be in the region of 8 and 20 bar (800 and 2000 kPa; 116 and 290 psi).
When it comes to textile lamination, IROGRAN® A 85 P 4394 HR TPU is an excellent material for creating a waterproof, breathable film in rugged performance apparel (including gloves and footwear). Blown to create an extremely thin layer, which is then added to fabrics, IROGRAN® A 85 P 4394 HR TPU provides the protective properties needed to create high performance outdoor garments. Adhering well to different kinds of fabrics, IROGRAN® A 85 P 4394 HR TPU can aid the stretch and recovery of the materials it is used on. The nature of the grade also means the resulting films can be engineered to have different surface finishes, including gloss, smooth and matte effects
Trent Shidaker, Global Marketing Director, Elastomers at Huntsman, said: “IROGRAN® A 85 P 4394 HR TPU is a highly versatile and durable elastomer. Soft to the touch, it’s ideal for apparel applications that need to stay in contact with the wearer for hours at a time; but it’s also strong enough to be used in municipal and industrial hoses that have to perform under the toughest conditions. Applying its development expertise, our elastomers team has enhanced the processing properties of IROGRAN® A 85 P 4394 HR TPU, without compromising the key performance attributes expected of products in this range – namely excellent hydrolytic resistance; fantastic wear performance; and microbial resistance. The result is an elastomer that can enable manufacturers to work more efficiently, cut waste and create longer-lasting products; a compelling proposition for the markets we serve.”
The basis of the chemistry of IROGRAN® A 85 P 4394 HR TPU goes back to 2004 when the flagship product was first developed. Later variations of the product were developed to create the family of elastomer products from Huntsman that customers have learned to know and love.
Other IROGRAN® A 85 P 4394 TPU products available from Huntsman include:
- IROGRAN® A 85 P 4394 – a legacy product, launched in 2004, that was first introduced for thin wall technical parts, thin wall extrusion profiles, spiral hoses, cable jacketing and film and sheet
- IROGRAN® A 85 P 4394 FCM – launched in 2015, this grade has a similar base chemistry to the standard version of IROGRAN® A 85 P 4394 but is formulated with raw materials that are compliant with FDA regulations for food processing belts and has an NSF 61 rating (approved for potable water applications).
- IROGRAN® A 85 P 4394 UV – also launched in 2015, this product is fortified with proprietary additives that enable it to withstand UV exposure while maintaining excellent physical properties and appearance. This product is used for pneumatic tubing for airlines and industrial equipment and fracking hoses.
IROGRAN® A 85 P 4394 HR TPU is made at the Huntsman Polyurethanes manufacturing facility in Ringwood Illinois. For more information about the full range of IROGRAN A 85 P 4394 TPU products available from Huntsman, please contact: joanna_marzec@huntsman.com.
June 21, 2021
Why you should never open unknown emails: Fighting ransomware attackers
Users — human beings — are the weakest link in even the ‘safest’ network
Published: June 20, 2021 19:30 Jay Hilotin, Senior Assistant Editor
Highlights
- Why ransomware attacks are spiking amid the COVID-19 pandemic.
- Know the top tips to avoid falling victim to darkweb attacks
- Know the dos and don’t of safe email practices.
Dubai: You think your network is “bomb-proof”? Or your organisation’s digital assets are “safe”? Think again. No matter how airtight you think work or organisation’s network is, there’s always a way in for the most persistent intruders. From the hackers’ point of view, we — the end users — are the best route of an hack. And this time, those who work from home are prized targets.
What’s the link between ransomware and pandemic?
Make no mistake: We are still in the midst of a health pandemic. And we’re also still in the midst of a digital pandemic of ransomware attacks. These are organised, deliberate attacks on increasingly significant targets. There are signs people and businesses are facing a chronic failure in finding ways to keep them at bay.
Why are ransomware attacks on the rise?
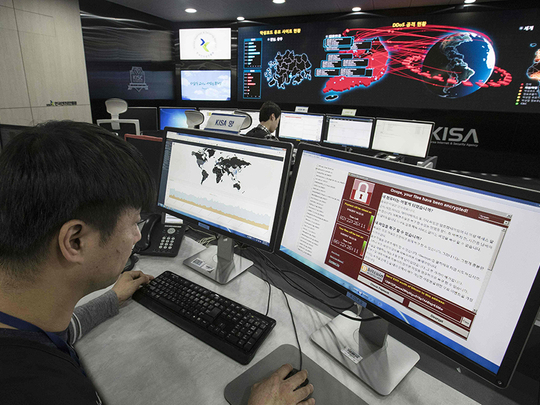
Ransomware attacks have spiked during the COVID-19 pandemic, say IT security professionals. “There’s one simple reason: More people are working away from the office, where security controls are comparatively weak,” said Anoop Kumar Pauval, Information Security Manager at Gulf News’ IT Department.
“At home, connected to work via remote data access, end-users tend to be less protected, and are more vulnerable,” Pauval added. He cited example, Check Point Research’s (CPR) latest report (published in May) found a 102% increase in ransomware attacks this 2021 compared to the beginning of 2020. “There are no signs of the attacks slowing down.”
What’s the usual route of a ransomware attack?
Most ransomware attacks exploit the vulnerabilities of employees to get through to organisation’s network. Most hacks are done this way, called “social engineering” attacks.
How do links pose a threat?
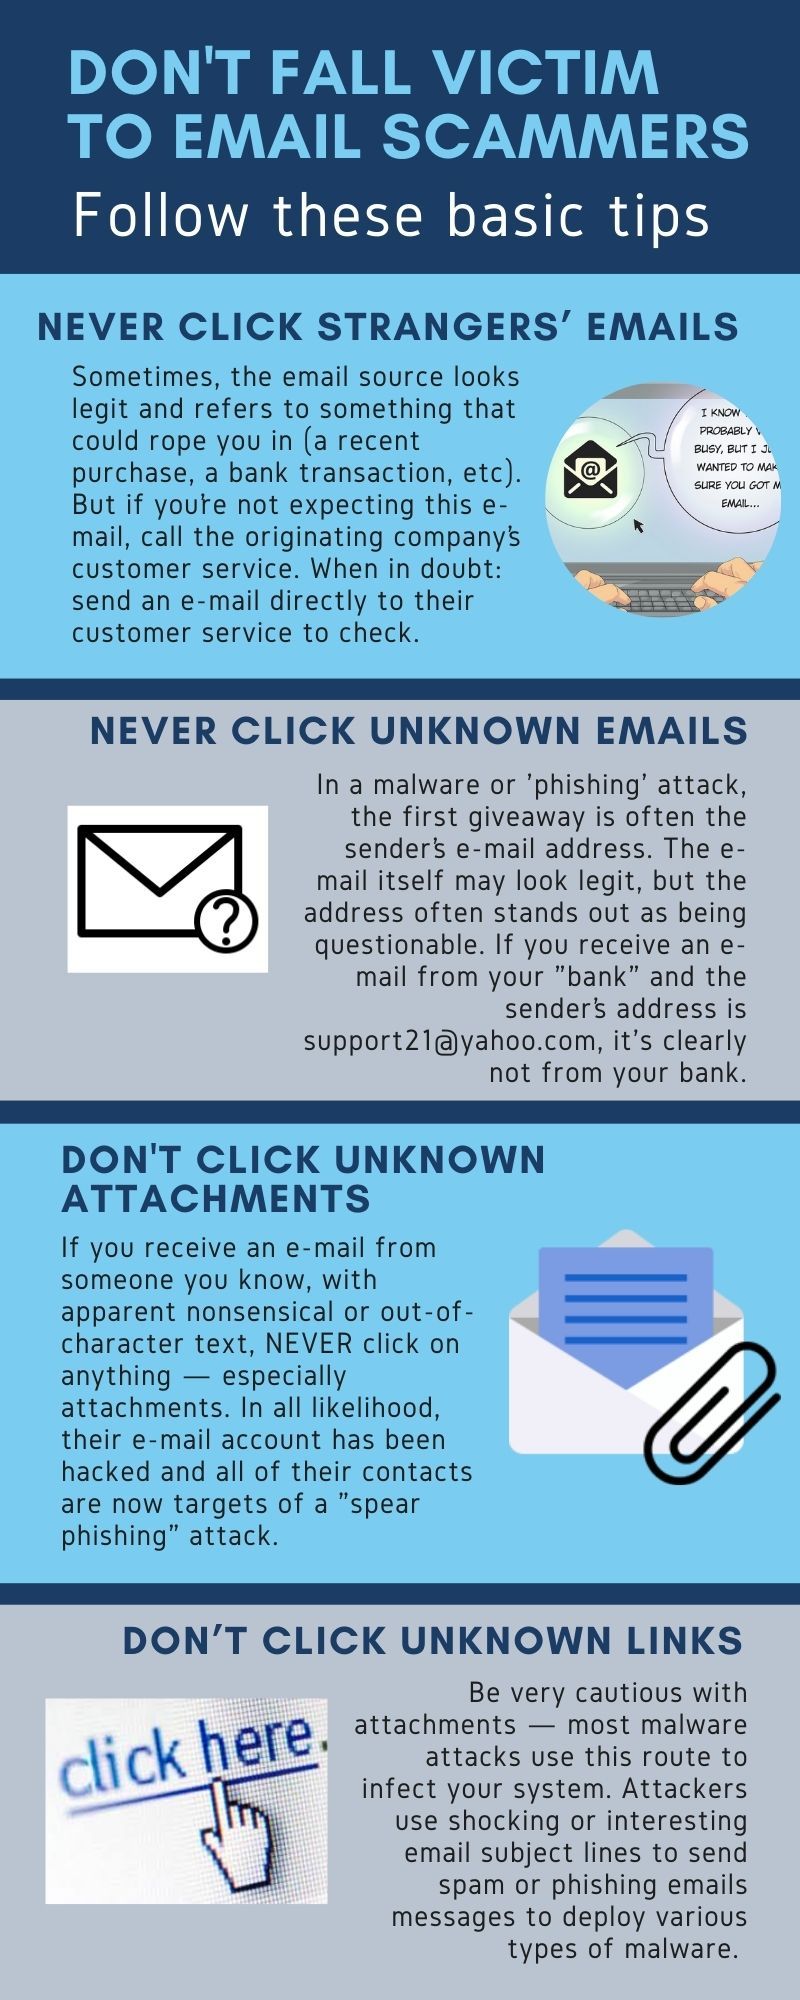
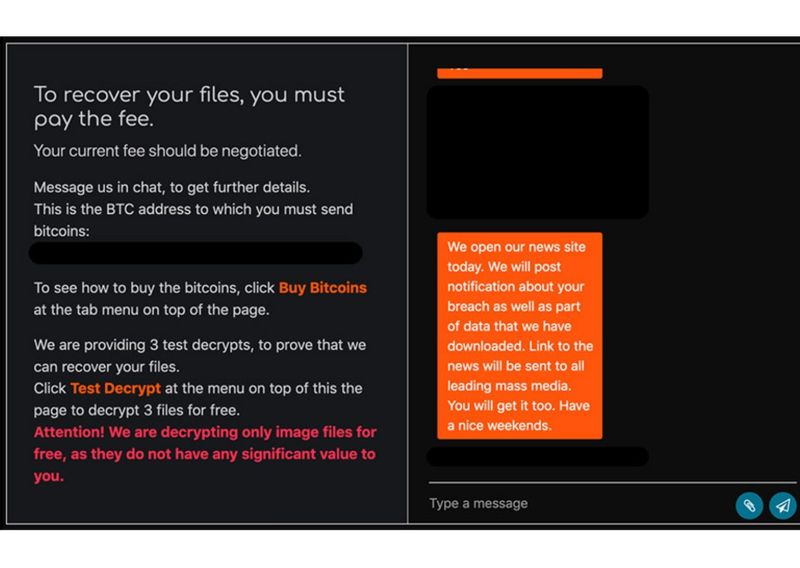
Emails are the most potent tools in the arsenal of cybercriminals. It comes int he form of a link or an attachment. If you open an unknown attachment or click a link in an email sent to you by a hacker, you’re roped in.
How can you tell the difference between legit email and hacker’s email?
There are email senders among people you know. They tend to be safer, but that’s not to say you shouldn’t exercise caution (especially with forwards). Some spams are obvious, but others are very smartly designed get past past the filters. They’re done by deception masters designed to dupe recipients. “Phishing” email is No. 1 way hackers get around firewalls, filters and antivirus.
Should I always trust emails from a friend or colleague?
No, even if it’s from a friend or colleague, take a pause before clicking anything further. Check the contents of the message they send along with it: Does it sound like it’s from them? A smarter way to avoid malware or phishing is to call the sender or speak in person, if possible, to confirm they sent the email. If you can’t be sure of its authenticity, simply delete.
Top 5 biggest ransomeware payouts:
 1. CWT Global ($4.5 million) | Date: July 2020 | The US travel services company CWT Global set a world record for the largest ever ransom payment, after it handed over $4.5 million in bitcoin to the Ragnar Locker ransomware gang. The attack is believed to have taken down 30,000 computers and compromised two terabytes of data. Financial records, security documentation and employees’ personal details, such as email addresses and salary data, were all affected. Image Credit: View gallery as list 1/5
Why are ransomware very disruptive?
The threat is real, as can be seen by recent examples. There’s often a financial motive involved. The demands are also real, too. But the damage to operations can destroy an institution or organisation’s reputation.
How much is the average ransomeware payment?
As we’ve seen, attacks capturing an organisation’s data and systems are on the rise. One study shows that since the start of the pandemic, ransomware attacks have gone up by almost 500%.
The average ransom payment has also continued to climb, up 43% from the last quarter of 2020 to an average of over $200,000, according to one report.
$200,000
the average ransomware payout during Q1 2021
Worse, a ransom demand is often accompanied by a breach and extraction of company data — and a concurrent extortion threatening to release this data unless additional payments are made.
News about attacks against the CNA Financial and Colonial Pipelines are recent publicly-known examples of hacking events. There’s a much bigger section involving unknown pay-offs for which the victims never publicly declare the hack.
Who are the perpetrators?
They are evolving, from the stand-alone hackers to what are now known as “criminal collectives”, including the DarkSide, which behave like state-sponsored attackers. These collectives have created virtual organisations, sharpening their techniques in targeting specific sectors and companies. They patiently wait for the kills.
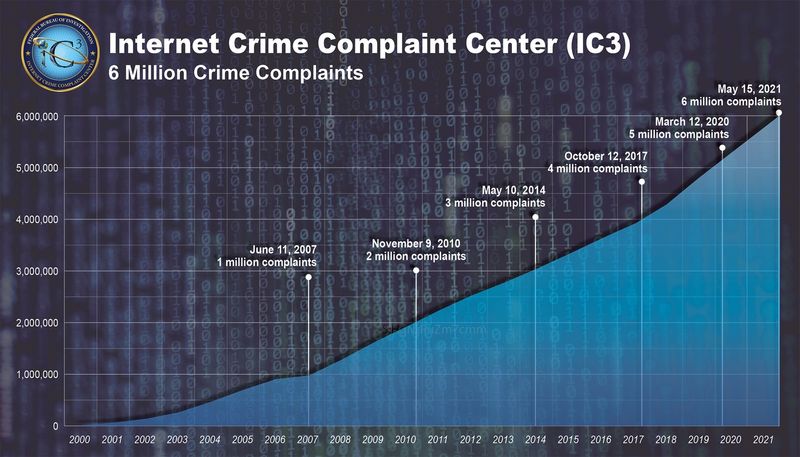
How big is the ‘cybercrime’ threat?
What’s the away around scams, spams and ransomware attacks.
It’s the dark underbelly of the online world. Cybercrime is a growing, highly successful and profitable “industry”. It is estimated that cybercrime costs will grow by 15% per year to reach $10.5 trillion by 2025. If it’s a country, it would be the world’s third-biggest “economy” — after those of the US States and China.
What’s the way around ransomware attacks?
Image when governments, health-care providers, online merchants like Amazon/ebay/Alibaba or other large organisations become beholden to cybercriminals? There’s certainly a way around the current state of affairs.
Intranets — closed, proprietary networks — might hold the key, say experts. As the internet evolves, a new trend emerges, with two distinct sides.
- Free-for-all internet:
This is the free-for-all, unfiltered, minimally regulated, “Wild West” type of internet anyone can access. This is the playground of the rising ranks of cybercriminals and everybody else, including you and me.
- Intranet
The second is “World Wide Intranet” — widely accessible but tightly controlled websites with stringent access controls to prevent criminal activity. Years ago, closed corporate intranets have gained popularity. This second type is rapidly evolving.
As such, as security measures and conditional access via multi-factor authentification will become a standard.
The internet needs a semblance of control — the price of not having them is immeasurably greater than the damage of any “restrictions”. It’s an inevitable outcome of the security threats mushrooming around us, compromising not only networks but individual the end users that use them.
June 21, 2021
Why you should never open unknown emails: Fighting ransomware attackers
Users — human beings — are the weakest link in even the ‘safest’ network
Published: June 20, 2021 19:30 Jay Hilotin, Senior Assistant Editor
Highlights
- Why ransomware attacks are spiking amid the COVID-19 pandemic.
- Know the top tips to avoid falling victim to darkweb attacks
- Know the dos and don’t of safe email practices.
Dubai: You think your network is “bomb-proof”? Or your organisation’s digital assets are “safe”? Think again. No matter how airtight you think work or organisation’s network is, there’s always a way in for the most persistent intruders. From the hackers’ point of view, we — the end users — are the best route of an hack. And this time, those who work from home are prized targets.
What’s the link between ransomware and pandemic?
Make no mistake: We are still in the midst of a health pandemic. And we’re also still in the midst of a digital pandemic of ransomware attacks. These are organised, deliberate attacks on increasingly significant targets. There are signs people and businesses are facing a chronic failure in finding ways to keep them at bay.
Why are ransomware attacks on the rise?
Ransomware attacks have spiked during the COVID-19 pandemic, say IT security professionals. “There’s one simple reason: More people are working away from the office, where security controls are comparatively weak,” said Anoop Kumar Pauval, Information Security Manager at Gulf News’ IT Department.
“At home, connected to work via remote data access, end-users tend to be less protected, and are more vulnerable,” Pauval added. He cited example, Check Point Research’s (CPR) latest report (published in May) found a 102% increase in ransomware attacks this 2021 compared to the beginning of 2020. “There are no signs of the attacks slowing down.”
What’s the usual route of a ransomware attack?
Most ransomware attacks exploit the vulnerabilities of employees to get through to organisation’s network. Most hacks are done this way, called “social engineering” attacks.
How do links pose a threat?
Emails are the most potent tools in the arsenal of cybercriminals. It comes int he form of a link or an attachment. If you open an unknown attachment or click a link in an email sent to you by a hacker, you’re roped in.
How can you tell the difference between legit email and hacker’s email?
There are email senders among people you know. They tend to be safer, but that’s not to say you shouldn’t exercise caution (especially with forwards). Some spams are obvious, but others are very smartly designed get past past the filters. They’re done by deception masters designed to dupe recipients. “Phishing” email is No. 1 way hackers get around firewalls, filters and antivirus.
Should I always trust emails from a friend or colleague?
No, even if it’s from a friend or colleague, take a pause before clicking anything further. Check the contents of the message they send along with it: Does it sound like it’s from them? A smarter way to avoid malware or phishing is to call the sender or speak in person, if possible, to confirm they sent the email. If you can’t be sure of its authenticity, simply delete.
Top 5 biggest ransomeware payouts:
1. CWT Global ($4.5 million) | Date: July 2020 | The US travel services company CWT Global set a world record for the largest ever ransom payment, after it handed over $4.5 million in bitcoin to the Ragnar Locker ransomware gang. The attack is believed to have taken down 30,000 computers and compromised two terabytes of data. Financial records, security documentation and employees’ personal details, such as email addresses and salary data, were all affected. Image Credit: View gallery as list 1/5
Why are ransomware very disruptive?
The threat is real, as can be seen by recent examples. There’s often a financial motive involved. The demands are also real, too. But the damage to operations can destroy an institution or organisation’s reputation.
How much is the average ransomeware payment?
As we’ve seen, attacks capturing an organisation’s data and systems are on the rise. One study shows that since the start of the pandemic, ransomware attacks have gone up by almost 500%.
The average ransom payment has also continued to climb, up 43% from the last quarter of 2020 to an average of over $200,000, according to one report.
$200,000
the average ransomware payout during Q1 2021
Worse, a ransom demand is often accompanied by a breach and extraction of company data — and a concurrent extortion threatening to release this data unless additional payments are made.
News about attacks against the CNA Financial and Colonial Pipelines are recent publicly-known examples of hacking events. There’s a much bigger section involving unknown pay-offs for which the victims never publicly declare the hack.
Who are the perpetrators?
They are evolving, from the stand-alone hackers to what are now known as “criminal collectives”, including the DarkSide, which behave like state-sponsored attackers. These collectives have created virtual organisations, sharpening their techniques in targeting specific sectors and companies. They patiently wait for the kills.
How big is the ‘cybercrime’ threat?
What’s the away around scams, spams and ransomware attacks.
It’s the dark underbelly of the online world. Cybercrime is a growing, highly successful and profitable “industry”. It is estimated that cybercrime costs will grow by 15% per year to reach $10.5 trillion by 2025. If it’s a country, it would be the world’s third-biggest “economy” — after those of the US States and China.
What’s the way around ransomware attacks?
Image when governments, health-care providers, online merchants like Amazon/ebay/Alibaba or other large organisations become beholden to cybercriminals? There’s certainly a way around the current state of affairs.
Intranets — closed, proprietary networks — might hold the key, say experts. As the internet evolves, a new trend emerges, with two distinct sides.
- Free-for-all internet:
This is the free-for-all, unfiltered, minimally regulated, “Wild West” type of internet anyone can access. This is the playground of the rising ranks of cybercriminals and everybody else, including you and me.
- Intranet
The second is “World Wide Intranet” — widely accessible but tightly controlled websites with stringent access controls to prevent criminal activity. Years ago, closed corporate intranets have gained popularity. This second type is rapidly evolving.
As such, as security measures and conditional access via multi-factor authentification will become a standard.
The internet needs a semblance of control — the price of not having them is immeasurably greater than the damage of any “restrictions”. It’s an inevitable outcome of the security threats mushrooming around us, compromising not only networks but individual the end users that use them.
 Everchem Updates Archive
 Sign Up for Email Updates